Welcome to SecureDrop’s documentation!#
SecureDrop is an open-source whistleblower submission system that media organizations can use to securely communicate with and accept files from anonymous sources. It is a free and open source source project of the Freedom of the Press Foundation (FPF), a US-based nonprofit organization.
SecureDrop connects journalists and their sources directly, in a way that substantially limits recorded metadata. Without third party intermediaries, SecureDrop helps protect potential sources, and puts news organizations in a strong position to challenge legal orders for data.
Note
This documentation is also available as a Tor Onion Service at http://dftlffjdogaragaxkc6jqxpo77s7rrngimyoq7uuq3clowhmttblcoyd.onion/en/stable/.
How it works#
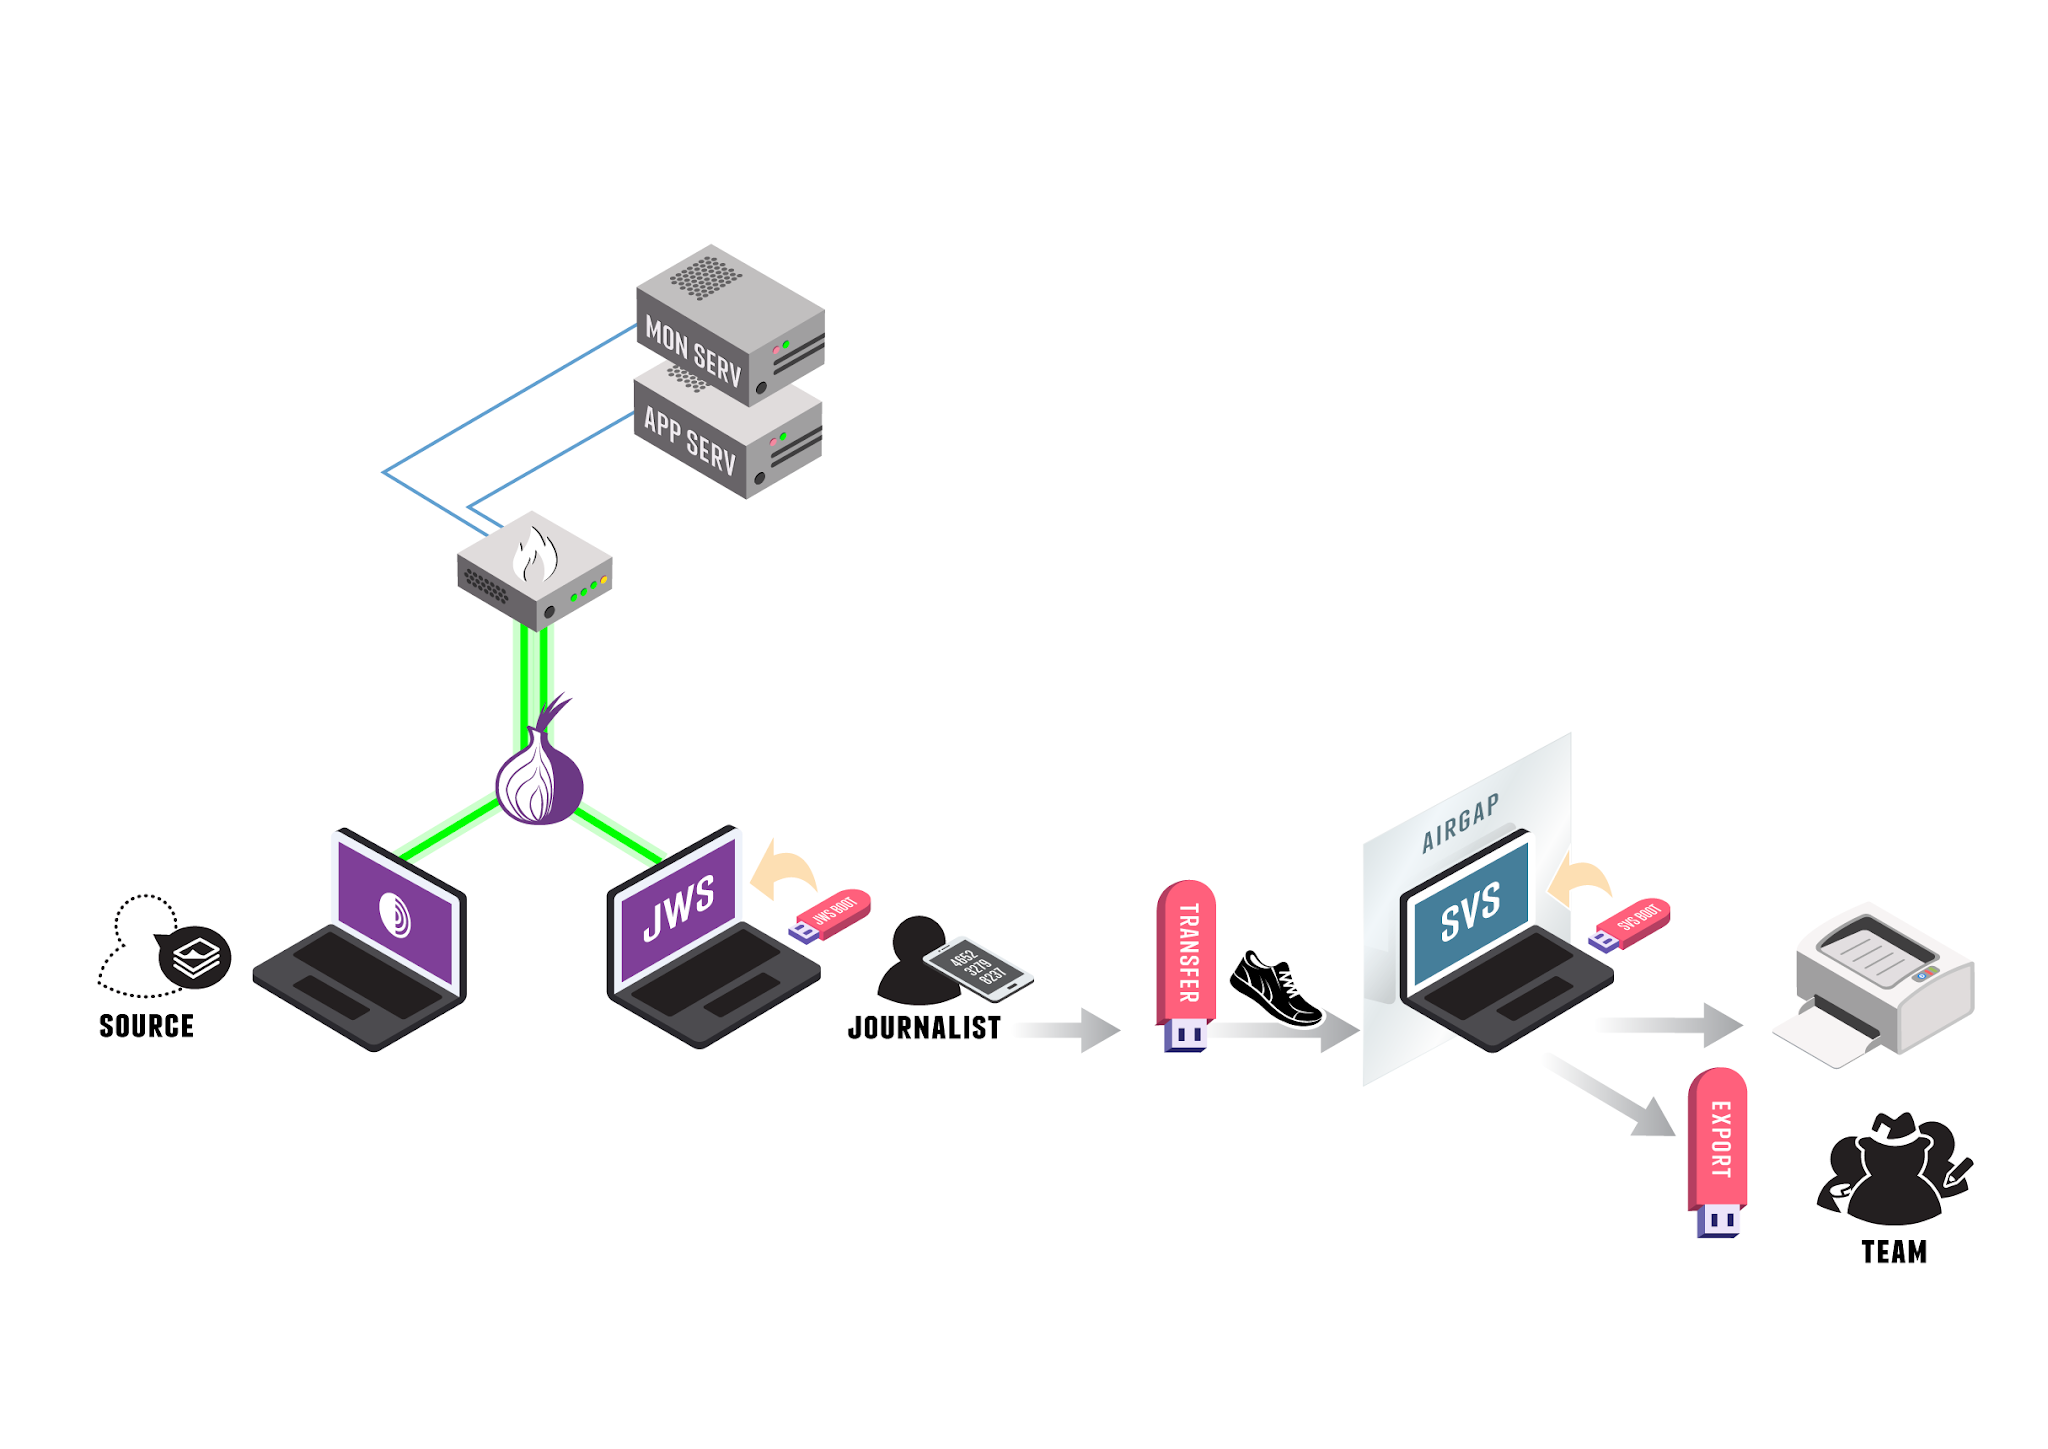
Sources and Journalists connect to SecureDrop using the Tor network. The SecureDrop software runs on-premises on dedicated infrastructure (two physical servers and a firewall).
The following steps describe how tips are submitted, received and reviewed using SecureDrop:
A Source sends a message or uploads a file to the news organization using Tor Browser.
A Journalist connects to SecureDrop using their SecureDrop Workstation, which provides separate isolated environments to view messages and download files before processing (e.g., to remove metadata or potential malware), printing, or exporting to a dedicated device.
See also
Check out What makes SecureDrop Unique to read more about SecureDrop’s approach to keeping Sources safe.
User roles#
There are three main user roles that interact with a SecureDrop instance:
- Sources
Submit files and messages using Tor Browser (or Tails) to access the Source Interface. Files and messages are encrypted on the Application Server as they are uploaded.
- Journalists
Use a SecureDrop Workstation to connect to SecureDrop and communicate with sources. Journalists download encrypted files and process them in an air-gapped environment.
- Admins
Manage the Application and Monitor Servers over authenticated onion services.
Note
The Glossary provides more-precise definitions of terms and concepts particular to SecureDrop. SecureDrop is designed against a comprehensive Threat model, and has a specific notion of the roles that are involved in its operation.
Infrastructure overview#
SecureDrop runs on two dedicated servers: the Application Server that hosts the Source and Journalist Interfaces, and the Monitor Server that runs an intrusion detection service and sends email alerts.
The servers operate on a segmented network connected directly to a dedicated hardware firewall.
A specially configured laptop, called a SecureDrop Workstation, is used by journalists to communicate with sources and safely handle submitted files. The same laptop, or one similarly configured, is also used by administrators to perform server maintenance.
SecureDrop is free to install, but requires hardware costing roughly $2,200–$2,400. See the hardware guide for supported and recommended equipment.
In addition to the hardware, you should make sure that you have the expertise necessary to operate and maintain SecureDrop. You’ll need a systems administrator or IT professional familiar with using a command-line interface within Linux.
The journalists in your organization will need to be trained in the operation of SecureDrop, and you’ll need to publish and promote your new SecureDrop instance afterwards using your existing websites, mailing lists, and social media.
It is recommended that you have all of this planned out before you get started. If you need help, contact the Freedom of the Press Foundation who will be glad to help walk you through the process and make sure that you’re ready to proceed.
Privacy and security#
While no system can guarantee 100% security, SecureDrop provides a number of safeguards and countermeasures to create a significantly safer environment for sources than standard channels.
Major architectural releases undergo third-party security audits; a full list of audits is available, along with a bug bounty program hosted by Bugcrowd.
SecureDrop routes all traffic to and from the server via the encrypted Tor network. Each SecureDrop server is completely owned by, and sits inside of, the news organization that operates it. SecureDrop minimizes metadata by not recording IP addresses, browser details, or computer information. It forces security best practices for journalists and can be used in high-risk environments.
Get involved#
SecureDrop is an open source project. You can support the work by contributing to SecureDrop or making a donation.